Introduction
The EU’s NIS2 Directive has turned cyber security from a “recommended IT line item” into a legal obligation backed by heavy fines across the European Union. In the UK the NIS Regulations 2018 cover operators of essential services, and the government’s Cyber Security and Resilience Bill is set to widen that scope in a similar direction.
If you run a corporate network, IT infrastructure or a manufacturing site – or you supply customers in the EU – you are probably already asking: how do we meet the new criteria without our hardware and software budget spiralling out of control?
This article looks at how the new rules affect the choice of network hardware, and why pairing industrial appliances with open-source firewall software is a cost-effective route for many businesses.
What does NIS2 expect from your network infrastructure?
Compared with the original directive, NIS2 covers far more sectors – from energy and healthcare to food production, logistics and digital providers. It also introduces supply-chain security: smaller firms that work with larger organisations are increasingly asked to prove a high level of protection. For practical network security, three steps stand out.
1. Strict network segmentation
Office PCs, accounting software, guest Wi-Fi and production machines can no longer share one flat network. If one device is compromised, the whole company becomes vulnerable. A capable hardware firewall that separates traffic physically and logically (VLANs) is the foundation.
2. Secure remote access and VPN encryption
With hybrid working, remote connections are a critical point. Every external connection to company resources should go through an encrypted VPN tunnel (for example WireGuard or OpenVPN) with two-factor authentication. That loads the router’s CPU heavily and calls for suitable hardware.
3. Business continuity
Security systems need high availability and failover. If the primary internet connection drops, the firewall should switch to a backup link automatically, without interrupting work.
The subscription trap: what a traditional hardware firewall really costs
When companies start looking for business cyber security, they usually turn to the big enterprise brands. There is a financial trap here: the subscription licensing model.
With a closed appliance you pay not only for the hardware but also an annual fee to activate features such as IPS/IDS, gateway antivirus and content filtering. If the licence lapses, the device stops receiving security definitions and loses much of its value. For many mid-sized businesses that is a heavy and unpredictable cost.
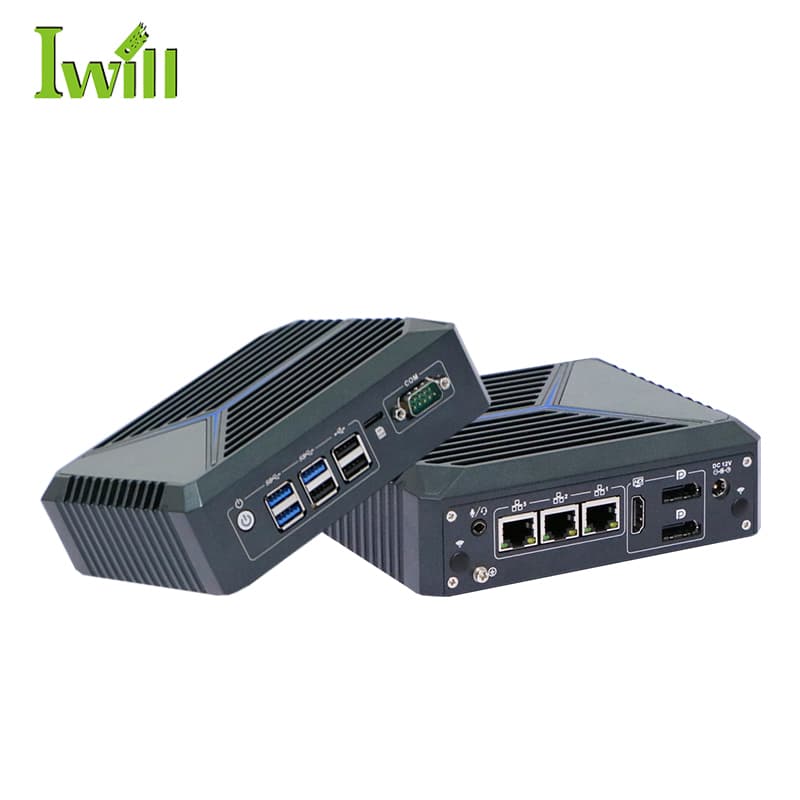
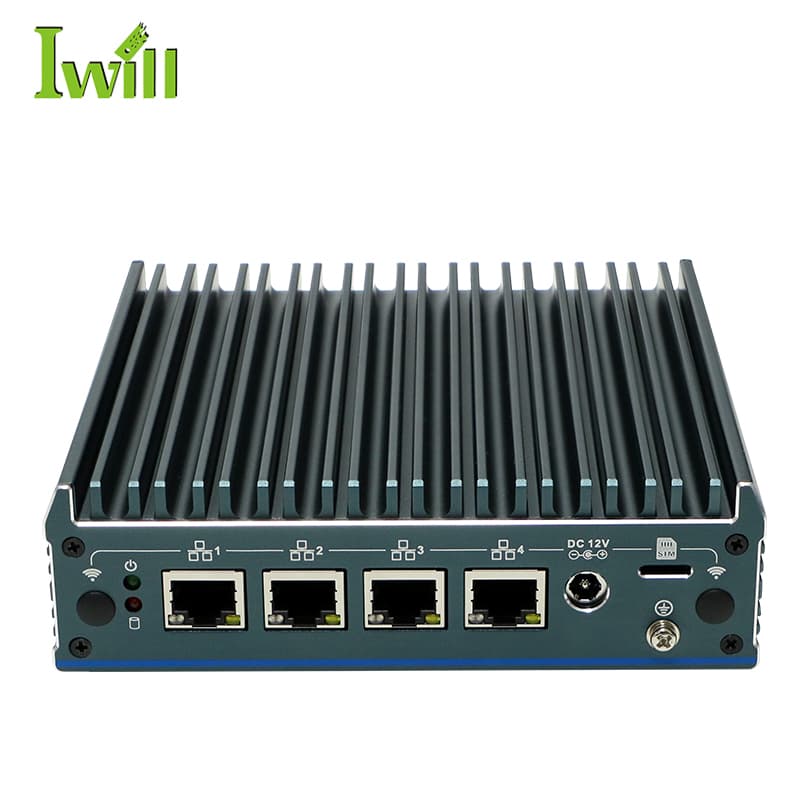
The alternative: dedicated OPNsense / pfSense hardware from IWILL
Can you address the technical measures behind NIS2 without expensive annual licences? For that part, yes: professional industrial hardware optimised for the leading open-source platforms pfSense and OPNsense supports measures such as network segmentation, access control and secure remote access. Compliance, however, also requires organisational measures, processes and documentation that no hardware covers.
No licence fees
You buy the hardware once. The software is open source, developed by a global community, updated regularly and offers enterprise-grade features free of charge.
Industrial reliability
Our appliances are fanless, with an all-aluminium chassis that acts as the heatsink. No fan means no failure from dust build-up or a seized bearing – directly relevant to continuity.
Intel performance
Multi-core Intel processors with AES-NI for fast VPN encryption and multiple Intel 2.5G LAN ports handle deep packet inspection and complex segmentation with ease.
Cyber security in manufacturing: protecting operational technology (OT)
NIS2 pays particular attention to industrial companies – food, pharmaceuticals, engineering. These environments often use standard office PCs to control expensive machines and SCADA systems, and those machines are the easiest way in for attackers.
Alongside network appliances, IWILL supplies industrial PCs. Our fanless mini PCs and industrial touch panels withstand dust, moisture, vibration and wide temperature ranges. Replacing consumer PCs on the shop floor with industrial machines supports production resilience and can form part of your technical measures – it is not, on its own, NIS2 compliance.
Related: for touch terminals in wet and hygiene-critical areas, see NIS2, IP65 and IP69 touch panels in food production.
Time to act: secure the business sensibly
Meeting NIS2 does not necessarily require huge budgets – it requires planning. Choosing IWILL hardware is an investment in long-term security, flexibility and independence while keeping IT costs under control.
- Browse our firewall and network security appliances.
- Compare the three tiers – N1121, N1241 and N3161 – on the network security solutions page.
- IT integrators, systems houses and consultants: contact us about partner terms.
Firewall and VPN appliances
Three tiers of fanless pfSense/OPNsense hardware for segmentation, VPN and failover.